Readiness Assessment

Don't guess readiness. Know what's missinginstantly.

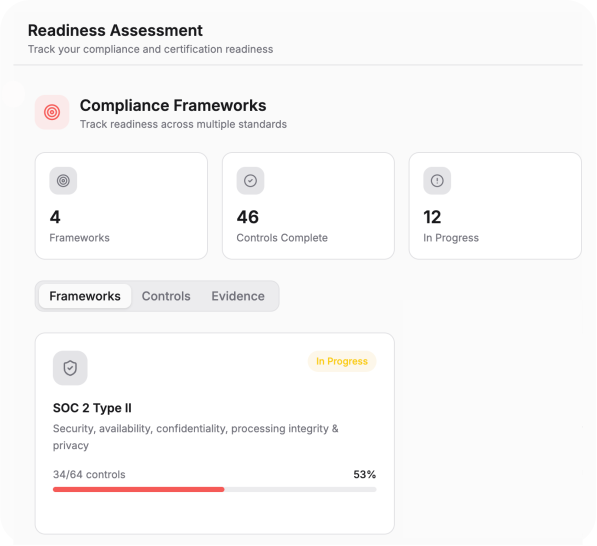
Pick any framework; 26Sunday gap-checks recommends fixes and tracks progress daily, with AI-enabled efficiency. Pre-mapped controls, auditor-approved evidence templates, and a clear gap closure plan.
https://app.26Sunday.com/readiness
Readiness Assessment Dashboard
5+
Frameworks supported + custom
70%
Faster audit preparation
100%
Gap visibility across controls
COMPLIANCE FRAMEWORKS

Pre-mapped controls, continuous audit gap-checks, and automated evidence templates tailored for high-growth enterprises.

+
+
+
+
INFOSEC BASELINE

ISO 27001

International standard for information security management.

ISOIEC 27001
+96,000 Global Certifications

More than 96,000 valid ISO 27001 certifications are in use globally, and adoption has nearly doubled between 2023 and 2024. The global average cost of a data breach reached $4.44 million in 2025; certification is a fraction of that exposure. ISO 27001 is not a nice-to-have anymore for B2B SaaS companies. It’s table stakes for enterprise procurement.

AI GOVERNANCE

ISO 42001

The first certifiable AI management system standard in the world.

ISOIEC 42001
+1,846% Certification Growth (2025–2026)

Adoptions increased 340% in 2025, and certifications grew 1,846% from April 2025 through March 2026. More than a quarter (28%) of U.S. firms now require suppliers to be ISO 42001 certified, up from just 2% in 2024. The EU AI Act is the rulebook; ISO 42001 is the operating system that makes compliance repeatable and auditable. This framework is the bridge between innovation and trust for any company building or deploying AI.

B2B SAAS STANDARD

SOC 2 Type II

The de facto B2B SaaS security baseline.

AICPASOCSOC 2®TYPE II REPORT
89% of Enterprise Buyers Require Prior to Signing

89% of Enterprise Buyers Require SOC 2 Type 2 Prior to Contract Signing. 73% of enterprise IT buyers will not consider vendors without a recent Type 2 report. For the Fortune 500, that number jumps to 98%. If you’re selling to enterprises, expect SOC 2 to appear in 80%+ of security questionnaires. Without it, you’re not only losing deals, but you’re also not even in the conversation.

DATA PRIVACY

GDPR

The gold standard for data privacy.

GDPREU 2016/679
€1.2B in 2025 Fines · 22% YoY Breach Rise

In 2025, European regulators issued over 300 fines totaling €1.2 billion. Daily data breach notifications increase 22% year-over-year. But only 15% of organizations are deemed “fully compliant”. Compliance with GDPR is not optional for any company that processes data of EU citizens. It is the price of doing business in one of the biggest markets in the world.

U.S. PRIVACY BLUEPRINT

CCPA

The blueprint for how U.S. states will regulate privacy.

CALIFORNIACCPACPRAPRIVACY ACT
$3.425B in 2025 State Privacy Penalties

U.S. state regulators imposed $3.425 billion in privacy-related penalties in 2025, nearly double the amount in 2024. Public penalties for CCPA/CPRA have topped over $23 million in high-profile cases as of early 2026. California is enforcing, and enforcing tough. If you serve CA residents, CCPA is the baseline, not the ceiling.

Custom Frameworks

HIPAA, NIST AI RMF, PCI DSS, ISO 27701, FedRAMP, or proprietary controls.

Bring Your Own Framework (BYOF)

Upload your control spreadsheets or audit guidelines. 26Sunday ingests and cross-maps controls directly into your readiness dashboard.

Report Generation

Audit-Ready Reports, Generated Instantly

Well-structured reports let you review and correct the security summary and help auditors understand compliance readiness. 26Sunday generates a complete readiness report with gap analysis, remediation plans, and evidence cross-references — formatted for your audit firm and board.

  • Executive Summary with Risk Heat Map and Readiness Score
  • A comprehensive gap analysis that includes estimates of effort and priority
  • A remediation roadmap that includes the proprietors, due dates, and dependencies
  • Evidence index with automatic cross-references to the source files

SOC 2 Readiness Report

0%

Readiness Score

4 critical gaps · 7 minor findings

01

Executive Summary

Risk Heat Map & Readiness Score

Ready
02

Gap Analysis Detail

Effort Estimates & Priority Matrix

Ready
03

Remediation Roadmap

Owners, Due Dates & Dependencies

Ready
04

Evidence Index

Auto Cross-Referenced Source Files

Ready
Total: 32 pages·PDF·Word

Everything you need to reach full audit readiness.

Six purpose-built capabilities to track, remediate, and prove compliance.

Pre-mapped control library

5 frameworks (ISO 42001, SOC 2, HIPAA, GDPR, NIST, PCI DSS) broken into precisely curated individual controls. Each control includes plain-English descriptions and auditor tips.

Cross-framework memory

Map a single control once, and it automatically applies to every framework that requires it. No duplicate work.

Gap scoring

Your dashboard shows actionable insight for each active framework. Understand exactly which controls are missing, partially complete, or ready.

Remediation plans

For each gap, the 26Sunday platform prioritizes step-by-step recommendations. Assign tasks to team members as required.

Structured auditor reports

Click a button to generate a complete readiness report: open gaps, evidence, and a smartly structured summary. Download as PDF or share a secure link.

Continuous re-assessment

Set a schedule (weekly, monthly, quarterly). The platform re-runs gap checks against your latest evidence and alerts you when scores change. Do your security pulse check beforehand.

Why Audit Readiness Needs More Than Automation

Find out where you stand on GRC audit readiness, and how 26Sunday takes compliance beyond automation to make it continuously actionable.

Market Sizing ($135.6B)Time & Cost BenchmarksContinuous Self-Audit Model